Apps · Security · AI Security
Software that earns trust.
i3cloud builds and publishes apps people rely on, and works on the security that keeps software like them honest.
Trust is the same problem everywhere. A family choosing where to eat. A student working through a surah. A parent handing a tablet to their child. A team giving an AI agent access to production. We build for all of them.
Published apps
Three products, in three very different worlds.
Security practice
The other half of the company.
Security
Solutions and products for software teams.
Application, cloud and identity security, built into how software ships.
Explore securityAI Security
Agents have credentials now. Treat them that way.
60 risks across 10 domains, from the SecureAI Daily atlas. Each one names the threat and the control.
See the risksAI security risks
Where trust in an AI tool actually breaks.
Ten domains from the SecureAI Daily atlas. Open one for the threat, and the control that contains it.
Data Security
Secrets leave in the prompt.
6 risks 02 IAMIdentity and Access
Agents are identities now.
6 risks 03 AGENTAgent Actions
One instruction, real damage.
6 risks 04 EXECAgentic Execution
The sandbox is the boundary.
6 risks 05 MCPMCP and Tools
Tool text is an attack surface.
6 risks 06 SUPPLYAI Supply Chain
The model is a dependency.
6 risks 07 NETNetwork Security
Egress is the last backstop.
6 risks 08 LOGSLogging and Monitoring
If you cannot replay it, you cannot trust it.
6 risks 09 WEBBrowser Security
The browser is an AI runtime.
6 risks 10 GOVGovernance
Policy has to hold when it breaks.
6 risksHow we build
Trust shown, not claimed.
- SpotHalal
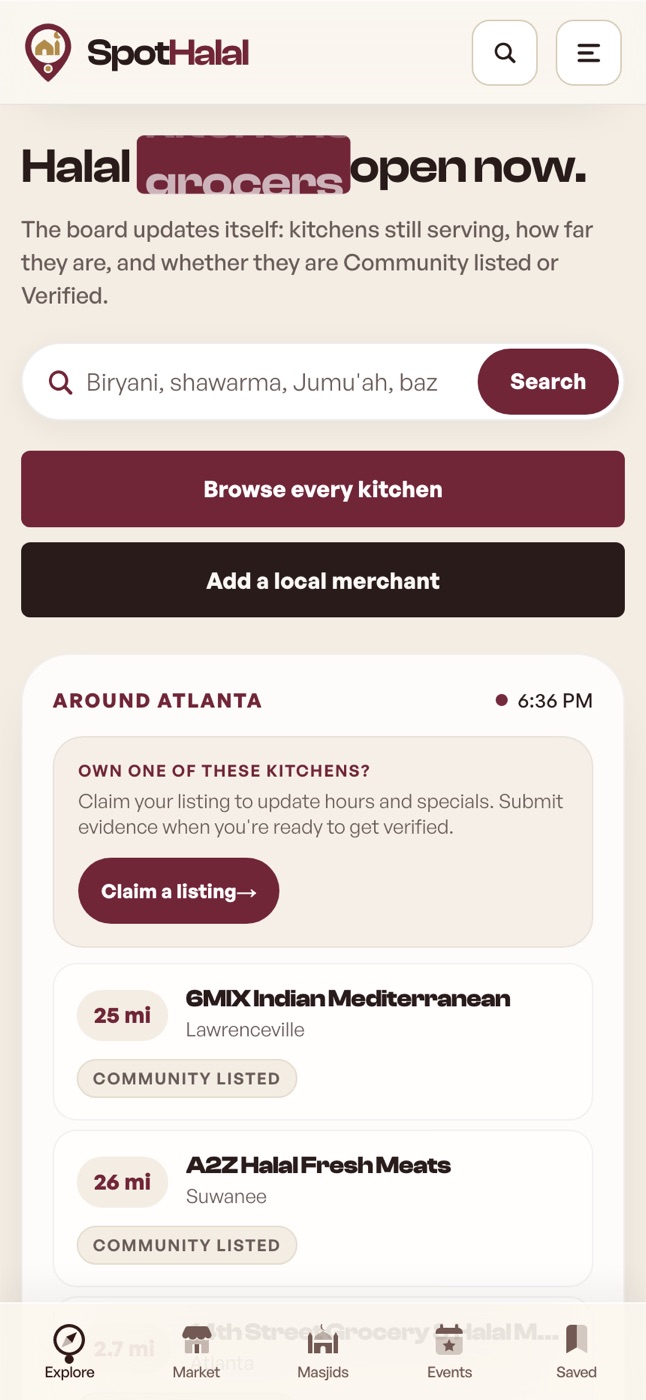
Every listing states its trust level, from community listed to verified, so you know before you go.
- Quran MindMaps
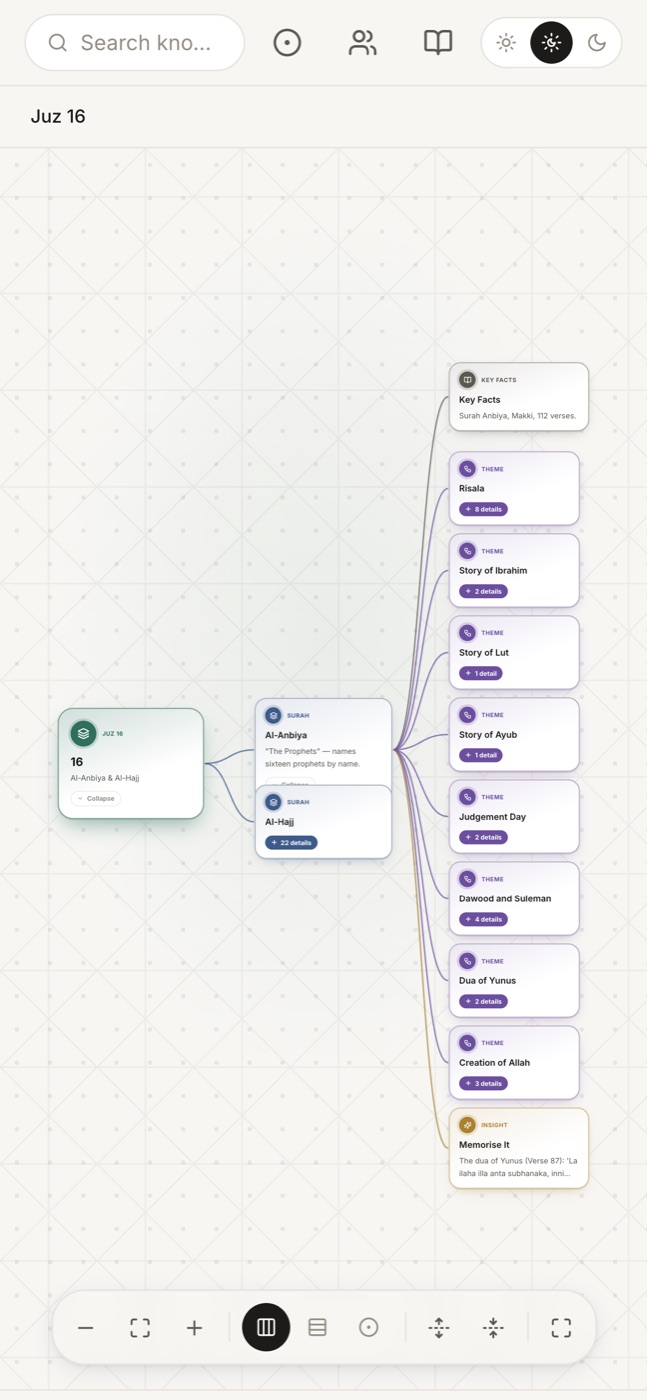
No accounts and no logins. Each map links back to the original hand-drawn poster it came from.
- Sprout Steps
Works fully offline with no accounts in the child's app. Nothing syncs unless a parent or teacher opts in with a pairing code.
- This website
No cookies, no third-party scripts, and a strict content security policy. Inspect the live headers.