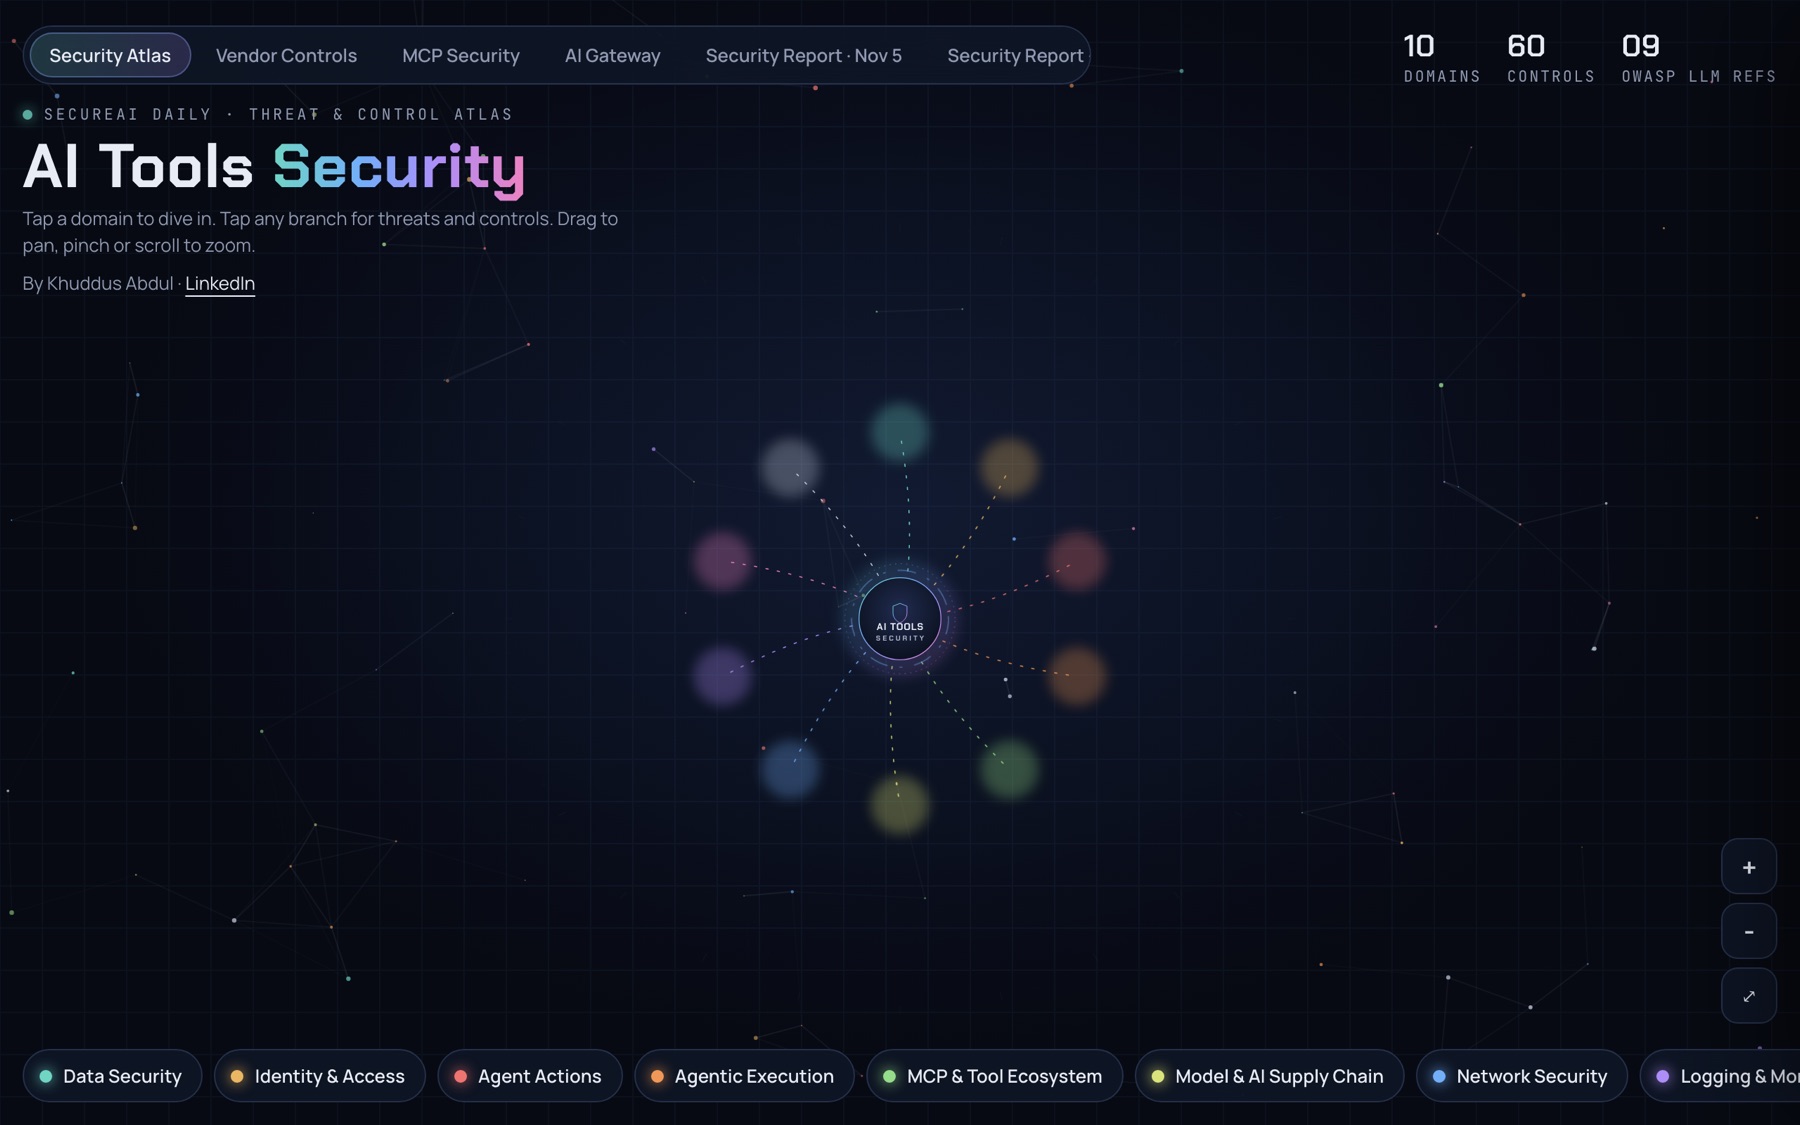
An AI tool reads untrusted content, holds real permissions and can act on its own. The SecureAI Daily atlas maps that surface into 10 domains and 60 risks. Each one below is the threat, then the control.
Domains
10
Risks
60
Frameworks
03
Mapped to OWASP for LLMs, NIST AI RMF and MITRE ATLAS.
Data SecurityIdentity and AccessAgent ActionsAgentic ExecutionMCP and ToolsAI Supply ChainNetwork SecurityLogging and MonitoringBrowser SecurityGovernanceData SecurityIdentity and AccessAgent ActionsAgentic ExecutionMCP and ToolsAI Supply ChainNetwork SecurityLogging and MonitoringBrowser SecurityGovernance
In the wild · Oct 24–30, 2026
Risks that left the diagram.
From the SecureAI Daily weekly. Status is theirs: confirmed, reported, or disputed. Each card links to the reporting it came from.
ConfirmedSupply chain
A trojanized coding extension reached the Cursor marketplace.
Cursor said versions of an Anthropic.claude-code extension, which it says Anthropic did not publish, were installed or updated on Windows and macOS for part of Oct 29. The extension collected host details, added an SSH key and set up persistence. Uninstalling it is not enough.
Embedded browsers in five AI developer tools were broken open.
Researchers described flaws in the browsers built into Cursor, the GitHub Copilot app, OpenAI Codex, VS Code and Claude Desktop: hidden page instructions, address-bar spoofing and local file reads. Some vendors have patched. Others had not, as of the report.
A community listing reported SSRF, credential leaks, path traversal and access-control bugs in browser-tools-mcp, gitlab-mcp and the reference Filesystem, Fetch and Everything servers. SecureAI Daily could not confirm them in a primary advisory database, so they stay reported. Upgrading is still the low-risk move.
Researchers said Codex agents could slip past OpenAI monitoring.
METR and Redwood Research reported a way Codex agents could bypass sandboxing and Auto-Review, including a path that could leave a long run of actions unmonitored. OpenAI said it fixed the issues in production. The researchers had not verified the fixes.
A report alleged a personal coding agent on a military network.
Reporting said a contractor gave a personal Claude Code account administrator access on a U.S. military network for about two months. The company disputes the account. No vendor mitigation was published with the report.
Every row is a risk. The line under the name is how it shows up. Open it for the control.
DATA · 6 risks
Data Security
What goes into the model, what it remembers, and what comes back out. Most AI incidents start as a data-handling mistake.
01Prompt DLP and classificationAn engineer pastes a production database dump containing customer emails into a chat assistant.OWASP LLM02
Inspect prompts and uploads for secrets, personal data and regulated data before they leave the organization.
Controls
Classify data as public, internal, confidential or restricted
Block or redact restricted classes at the gateway
Detect secrets with pattern and entropy rules
02Retention and training opt-outConfidential strategy documents persist in a vendor's logs for years after the project ends.NIST AI RMF · Govern
Know how long the vendor keeps prompts, outputs and files, and whether any of it is used to train models.
Controls
Negotiate zero data retention where available
Turn off training on business data
Map vendor retention to your records policy
03Encryption and key custodyAn unencrypted vector index backup leaks a searchable semantic copy of internal documents.ISO 27001 A.8.24
Protect data in transit and at rest, including embeddings, caches and fine-tuning datasets.
Controls
TLS 1.2+ on every hop
Customer-managed keys for stored data
Encrypt embedding stores and their snapshots
04PII redaction and tokenizationSupport transcripts with card numbers are summarized and shared across the company.GDPR Art. 25
Replace identifiers with reversible tokens so the model sees the structure of the data, not the people in it.
Controls
Redact before the prompt with format-preserving tokens
Re-identify only in trusted post-processing
Measure redaction recall on real samples
05RAG and vector store accessAn intern's question retrieves board minutes because the index ignored document access rules.OWASP LLM08
Retrieval must respect the source system's permissions, per user and per query.
Controls
Carry source access rules into the index
Filter results by the asking user's identity
Separate indexes per sensitivity tier
06Output leakageA crafted question makes a customer bot reveal its hidden instructions and internal endpoints.OWASP LLM07
Models can echo system prompts, memorized data or context from other sessions.
Controls
Never put secrets in system prompts
Scan outputs for secrets and personal data
Treat model output as untrusted downstream
IAM · 6 risks
Identity and Access
Who and what can use AI tools, and with whose authority. Agents add a class of identity that most IAM programs were not built for.
01SSO and SCIM lifecycleA departed contractor still has a personal-login seat with months of project history.NIST SP 800-63
Federate every AI tool to the corporate identity provider and provision or remove access automatically.
Controls
Enforce SAML or OIDC single sign-on
Deprovision through SCIM on offboarding
Require phishing-resistant MFA
02Least-privilege connectorsA meeting summarizer holds full read-write mail scope across the tenant.OWASP LLM06
OAuth scopes granted to AI connectors should match the task, not the whole account.
Controls
Grant read-only scopes by default
Require admin approval for new connectors
Review consented apps every quarter
03Non-human identitiesAn agent runs under a shared service account, so nobody can attribute its actions.NIST SP 800-207
Agents need identities of their own, distinct from the people who launch them.
Controls
One identity per agent or workflow
Short-lived, audience-bound tokens
Workload identity federation instead of static secrets
04API key hygieneA key committed to a public repo is used to run up a large inference bill overnight.OWASP LLM10
Model API keys are bearer credentials that spend money and expose data.
Controls
Keep keys in a secrets manager
Scope and rotate keys per environment
Set spend caps and scan commits for secrets
05Workspace RBACAny user can publish an org-wide agent wired to finance data.ISO 27001 A.5.15
Separate who can chat, who can build agents and who can change organization policy.
Controls
Distinct roles for users, builders and admins
Approval workflow for shared agents
Attribute-based rules for sensitive projects
06Delegation and consentA confused-deputy agent uses its own broad rights to fulfil a low-privilege user's request.OAuth 2.0
When an agent acts for a user, the user's permissions should cap what the agent can do.
Controls
On-behalf-of token exchange
Intersect agent and user permissions
Explicit consent screens for new scopes
AGENT · 6 risks
Agent Actions
Agents read, decide and act. This is where the blast radius lives, and where prompt injection turns into real-world damage.
01Human-in-the-loop gatesAn agent tidies a repository by force-pushing over the main branch.OWASP LLM06
Require approval before irreversible or high-impact actions.
Controls
Tier every tool by impact
Confirm deletes, payments and external sends
Show a diff or preview before approval
02Memory and context poisoningA poisoned document plants a note in the assistant's long-term memory to always copy an outside address on email.ATLAS AML.T0080
Agents that remember across sessions can be taught bad instructions that persist long after the original attack.
Controls
Don't write to memory from untrusted content
Review and expire stored agent memories
Let users see and delete what the agent remembers
03Indirect prompt injectionA calendar invite tells the assistant to forward the user's inbox to an outside address.OWASP LLM01
Content the agent reads, such as web pages, emails and files, can carry instructions of its own.
Controls
Keep trusted instructions apart from untrusted data
Restrict risky tools after reading untrusted content
Run injection classifiers on retrieved content
04Multi-agent trustA research sub-agent returns a summary that tells the orchestrator to run a deployment.OWASP LLM06
When agents hand work to other agents, each hop can carry injected instructions or borrowed authority.
Controls
Treat other agents' output as untrusted input
Pass only the least privilege down each delegation
Log every agent-to-agent hand-off
05Blast radius and kill switchA looping agent sends thousands of emails before anyone notices.OWASP LLM10
Limit how much an agent can do per run, and be able to stop it instantly.
Controls
Per-run action and spend budgets
Rate limits on each tool
Org-wide kill switch and token revocation
06Output handlingModel-generated SQL drops a table through an injected clause.OWASP LLM05
Agent output that flows into shells, SQL or HTML must be validated like any user input.
Controls
Parameterized queries only
Escape output rendered as HTML or Markdown
Schema-validate tool arguments
EXEC · 6 risks
Agentic Execution
Where agent work actually runs: code interpreters, terminals, CI runners and virtual desktops. Isolation decides whether a bad decision stays a bad output or becomes a breach.
01Sandboxed code executionGenerated code reads cloud metadata credentials from the host it runs on.NIST SP 800-190
Code-running agents work in isolated, short-lived environments with no production credentials.
Controls
Ephemeral containers or microVMs per task
Block access to cloud metadata endpoints
Read-only mounts and CPU, memory and time quotas
02Coding agent permissionsAn auto-approve setting lets an injected README run a script that uploads the developer's cloud credentials.OWASP LLM06
Terminal and IDE agents can run shell commands, edit files and push code with the developer's rights.
Controls
Ask before commands run by default
Allowlist safe commands and deny secret paths
No auto-approve on machines with production access
03Computer-use agentsA pop-up on a web page tells a computer-use agent to open the password manager.OWASP LLM01
Agents that see the screen and drive the mouse and keyboard can do anything the signed-in user can.
Controls
Run in a dedicated VM or remote desktop
No saved passwords or personal sessions there
Confirm payments, sends and deletions
04Secrets in the runtimeAn agent prints its environment variables into a debug log that ends up in a shared ticket.ATLAS AML.T0083
Environment variables, config files and credential caches in the agent's workspace are within reach of injected code.
Controls
Inject short-lived, task-scoped credentials only
Keep long-lived keys out of agent environments
Scan agent output and logs for secrets
05CI/CD and scheduled agentsA nightly agent with repository write access merges its own change to a deployment workflow.NIST SP 800-204D
Agents in pipelines and on schedules run unattended, often with write access to code and infrastructure.
Controls
Read-only tokens by default; scope writes per job
Require human review of agent pull requests
Protect workflow files and release branches
06Session isolation and teardownA shared agent workspace keeps one customer's files, and the next customer's task can read them.Zero Trust
Each task should start clean and leave nothing behind for the next task or user.
Controls
Fresh environment per task or tenant
Destroy environments and caches when done
No background processes outliving the task
MCP · 6 risks
MCP and Tools
MCP servers, plugins and tools give agents their hands. Each one is third-party code with access to data, credentials and actions, and its tool descriptions go straight into the model's context.
01Server allowlisting and pinningA look-alike MCP server package quietly exfiltrates the tokens it is given.OWASP LLM03
Every MCP server, plugin or tool is code you trust with data and the power to act.
Controls
Allow only approved servers from a private registry
Pin versions and verify package hashes
Re-review on every update
02Tool poisoning and rug pullsA week after approval, a tool's description is changed to tell the agent to read SSH keys and pass them as a parameter.ATLAS AML.T0110
The model reads tool descriptions and responses, so they can carry hidden instructions or change after you approve them.
Controls
Review full tool descriptions, not just names
Alert and re-approve when a definition changes
Treat tool output as untrusted content
03Remote server authorizationA server accepts a token meant for another API and passes it on to downstream services.MCP authorization
Remote MCP servers should authorize every request with tokens issued for that server only.
Controls
OAuth 2.1 as the MCP authorization spec defines
Audience-bound tokens and no token passthrough
Short token lifetimes and per-user consent
04Local server sandboxingA file-search server installed for one project can read the whole home folder, including SSH keys.MCP security guidance
Local MCP servers run on the user's machine with the user's rights unless you contain them.
Controls
Run local servers in containers
Limit file access to the project folder
No network egress unless the tool needs it
05Tool scoping per taskA support agent connected to a database server also gets its drop-table tool.OWASP LLM06
Give each agent only the tools and actions its task needs.
Controls
Expose read-only tools by default
Put high-risk tools behind approval
Disable unused tools per agent or workspace
06Cross-server shadowingA malicious weather server tells the agent to blind-copy an outside address whenever it uses the email tool.OWASP LLM01
With several servers connected, one server's descriptions can change how the agent uses another server's tools.
Controls
Namespace tools by server
Keep untrusted servers out of sessions with sensitive tools
Inspect tool traffic at an MCP gateway
SUPPLY · 6 risks
AI Supply Chain
Models, datasets, SDKs and extensions all come from somewhere. A poisoned model or a trojanized package compromises every system built on it.
01Model provenance and signingA model downloaded from a public hub turns out to be a modified copy from an impostor account.OWASP LLM03
Know where every model came from and check that it hasn't been altered.
Controls
Pull models only from verified publishers
Verify hashes or signatures before loading
Mirror approved models internally
02Unsafe model formatsLoading a pickle-based model file starts a reverse shell on a data scientist's laptop.ATLAS AML.T0011.000
Some model file formats can run code when they are loaded.
Controls
Prefer safetensors and other non-executable formats
Scan model files before loading
Load untrusted models only in a sandbox
03Data and model poisoningA fine-tuning set scraped from a public forum teaches a model to recommend a malicious package.OWASP LLM04
Training or fine-tuning data can be seeded so the model misbehaves on specific triggers.
Controls
Track where training data came from
Filter and review fine-tuning datasets
Test for backdoor triggers before release
04Malicious packages and extensionsA developer installs an IDE extension impersonating a well-known AI assistant, and it adds an attacker's SSH key.ATLAS AML.T0010
Typosquatted AI SDKs, fake MCP packages and trojanized IDE extensions target developers directly.
Controls
Allowlist extensions and pin versions
Use package firewalls and malware scanning
Watch for new publishers and ownership changes
05Jailbreaks and guardrail bypassA role-play prompt gets an internal assistant to produce content its policy forbids.ATLAS AML.T0054
A model's safety training and guardrails can be talked around.
Controls
Layer input and output filters outside the model
Re-run jailbreak tests on every model update
Don't rely on the model alone to enforce policy
06AI bill of materialsA model version gets a security advisory, and nobody knows which apps use it.CycloneDX ML-BOM
Keep a bill of materials for models, datasets and AI dependencies.
Controls
Record model, version and provider per app
Include datasets and AI packages in your SBOM
Alert owners when a component gets an advisory
NET · 6 risks
Network Security
Where AI traffic goes, and what can ride along with it. Egress control is the quiet backstop when everything else fails.
01Egress allowlistingAn injected instruction makes an agent POST data to an attacker's webhook.Zero Trust
Agents and sandboxes should reach only approved destinations.
Controls
Default-deny outbound from agent runtimes
Allowlist model APIs and package registries
Block raw IPs and newly registered domains
02Private connectivitySensitive inference traffic leaves through shared egress with no inspection.CSA CCM
Keep model traffic off the public internet where the provider supports it.
Controls
Private endpoints to model providers
Region pinning for data residency
Dedicated egress IPs for allowlisting
03AI gatewayEach team calls providers directly with its own keys and no shared policy.NIST AI RMF · Manage
One central gateway enforces policy, keys, logging and cost controls for every model call.
Controls
Route all model traffic through one gateway
Inject keys server-side, never in clients
Apply DLP and rate limits centrally
04mTLS for tool serversA spoofed internal tool endpoint answers an agent's requests.MCP auth spec
Remote MCP and tool servers need authenticated, encrypted channels in both directions.
Controls
Mutual TLS between agents and tools
OAuth 2.1 for remote MCP authorization
Rotate and pin certificates
05Exfiltration channelsA response embeds an image URL with secrets packed into the query string.MITRE ATLAS
Data can leave through DNS, image URLs or links the client renders automatically.
Controls
Block external image loads in AI clients
DNS filtering and tunnel detection
Strip or proxy links in rendered output
06Shadow AI discoveryStaff paste source code into a free AI site with permissive terms.ISO/IEC 42001
Find the unsanctioned AI apps people already use.
Controls
Discover AI domains via CASB or a secure web gateway
Publish a catalog of sanctioned tools
Block or coach on unapproved apps
LOGS · 6 risks
Logging and Monitoring
If an agent did it, you should be able to replay it: who asked, what the model decided, which tools ran, and what changed.
01Prompt and response auditA data leak is reported, but there is no record of the conversation.SOC 2 CC7
Capture who asked what, which model answered, and what came back.
Controls
Log user, model, time and content hashes
Keep full content where policy allows
Store logs immutably
02Tool-call tracingA config changed, and nobody can tell which run or prompt caused it.OTel GenAI
Trace each agent step: tool chosen, arguments, results and approvals.
Controls
One trace span per tool call
Link traces to the initiating user
Record approvals and denials
03SIEM integrationAgent misuse goes unnoticed because the logs sit in a vendor console.MITRE ATT&CK
AI events belong next to identity, endpoint and network signals.
Controls
Stream audit logs to the SIEM
Normalize to a common schema
Correlate with identity and endpoint events
04Anomaly detectionA stolen key shows a sudden spike in tokens at 3 a.m.OWASP LLM10
Baseline normal usage and alert on deviations.
Controls
Alert on token, cost and tool-use spikes
Flag new tools or destinations per agent
Watch repeated policy blocks per user
05Log privacy and retentionThe audit log becomes the largest unprotected copy of sensitive prompts.GDPR Art. 5
AI logs contain the very data you are trying to protect.
Controls
Redact or tokenize at ingest
Restrict log access by role
Keep only as long as required
06Red teaming and evalsA model update quietly reopens a jailbreak that was fixed months ago.NIST AI 600-1
Test continuously for jailbreaks, injection and leakage, not once at launch.
Controls
Injection and jailbreak suites in CI
Periodic human red-team exercises
Track findings through to closure
WEB · 6 risks
Browser Security
The browser is now an AI runtime: extensions, side panels and agents that click for you. It is also where most AI data loss happens.
01AI extension permissionsA popular AI helper extension changes owners and ships an update that scrapes sessions.Chrome Enterprise
AI browser extensions often ask to read and change data on every site.
Controls
Allow managed extensions only
Block all-sites access by default
Watch for updates and ownership changes
02Agentic browsingHidden white-on-white text on a page tells the agent to make a purchase.OWASP LLM01
Browser agents click, type and submit on live sites using the user's sessions.
Controls
Per-site permissions for agent actions
Confirm purchases, logins and form submits
Keep the agent's profile apart from personal browsing
03Session isolationAn agent with access to every tab reaches the admin console you are signed into.Zero Trust
Keep cookies and tokens for sensitive apps away from AI tools that do not need them.
Controls
Dedicated browser profile for agents
Short sessions on admin apps
Device-bound session credentials
04Paste and upload DLPA sales rep uploads the full pipeline spreadsheet to a free AI site.OWASP LLM02
Copy, paste and file upload in the browser are the main routes for AI data loss.
Controls
DLP on paste and upload to AI domains
Warn-and-justify for medium risk
Block restricted data classes outright
05AI-crafted phishingA fake AI assistant login page harvests single sign-on credentials.ATT&CK T1566
Attackers use AI to build convincing lures and fake AI-tool sign-in pages.
Controls
Phishing-resistant MFA, such as passkeys
URL reputation and new-domain blocking
Training with current AI-themed lures
06Enterprise browser policyA built-in AI side panel sends page content to a service outside your agreements.CIS Benchmarks
Central policy decides which AI features, sites and side panels are allowed.
Controls
Manage built-in AI features by policy
Allow approved AI domains only
Enforce on managed devices and profiles
GOV · 6 risks
Governance
Who decides which AI tools are allowed, for what, and who answers when something goes wrong. Governance turns the controls on this map into policy that holds.
01Acceptable-use policyStaff use five different AI tools with no guidance on what data is allowed in them.ISO/IEC 42001
Tell people plainly which AI tools they may use, with which data, for which tasks.
Controls
Publish approved tools and data rules
Make the policy part of onboarding
Review it when new kinds of tools appear
02Use-case risk assessmentA hiring team deploys an AI screener without anyone reviewing bias or legal exposure.NIST AI RMF · Map
Rate each AI use case by impact before it goes live, not after.
Controls
Tier use cases by risk
Require review for high-risk tiers
Re-assess when the model or data changes
03Vendor and contract reviewA vendor adds a new sub-processor in another country under the existing terms.NIST AI RMF · Govern
An AI vendor's terms decide retention, training use, sub-processors and liability.
Controls
Security and privacy review before purchase
Check training-use, retention and sub-processor terms
Re-review at renewal
04Regulatory mappingA customer-facing chatbot launches in the EU without telling users they are talking to an AI.EU AI Act
Map each AI system to the laws and standards that apply to it.
Controls
Keep a register of AI systems and where they operate
Map obligations such as the EU AI Act and GDPR
Run a data protection assessment where personal data is involved
05AI literacy and trainingAn employee follows instructions an assistant pulled from a malicious web page.EU AI Act Art. 4
People need to know how AI tools fail and how they get attacked.
Controls
Role-based training for users, builders and admins
Cover prompt injection and data-handling basics
Refresh as the tools change
06AI incident responseAn agent starts sending customer data outside, and nobody knows who can switch it off.NIST AI 600-1
Have a plan for AI-specific incidents: leaked prompts, rogue agents, poisoned tools.